Digital sovereignty: why the Cloud Act changes your architecture
Where your recordings live has stopped being a technical decision. It is a decision about legal exposure, and it belongs to the board.
Read article →Sovereignty
An interaction does not have to be preserved where it is processed. Separating the two gives the organisation back control over its customer history.
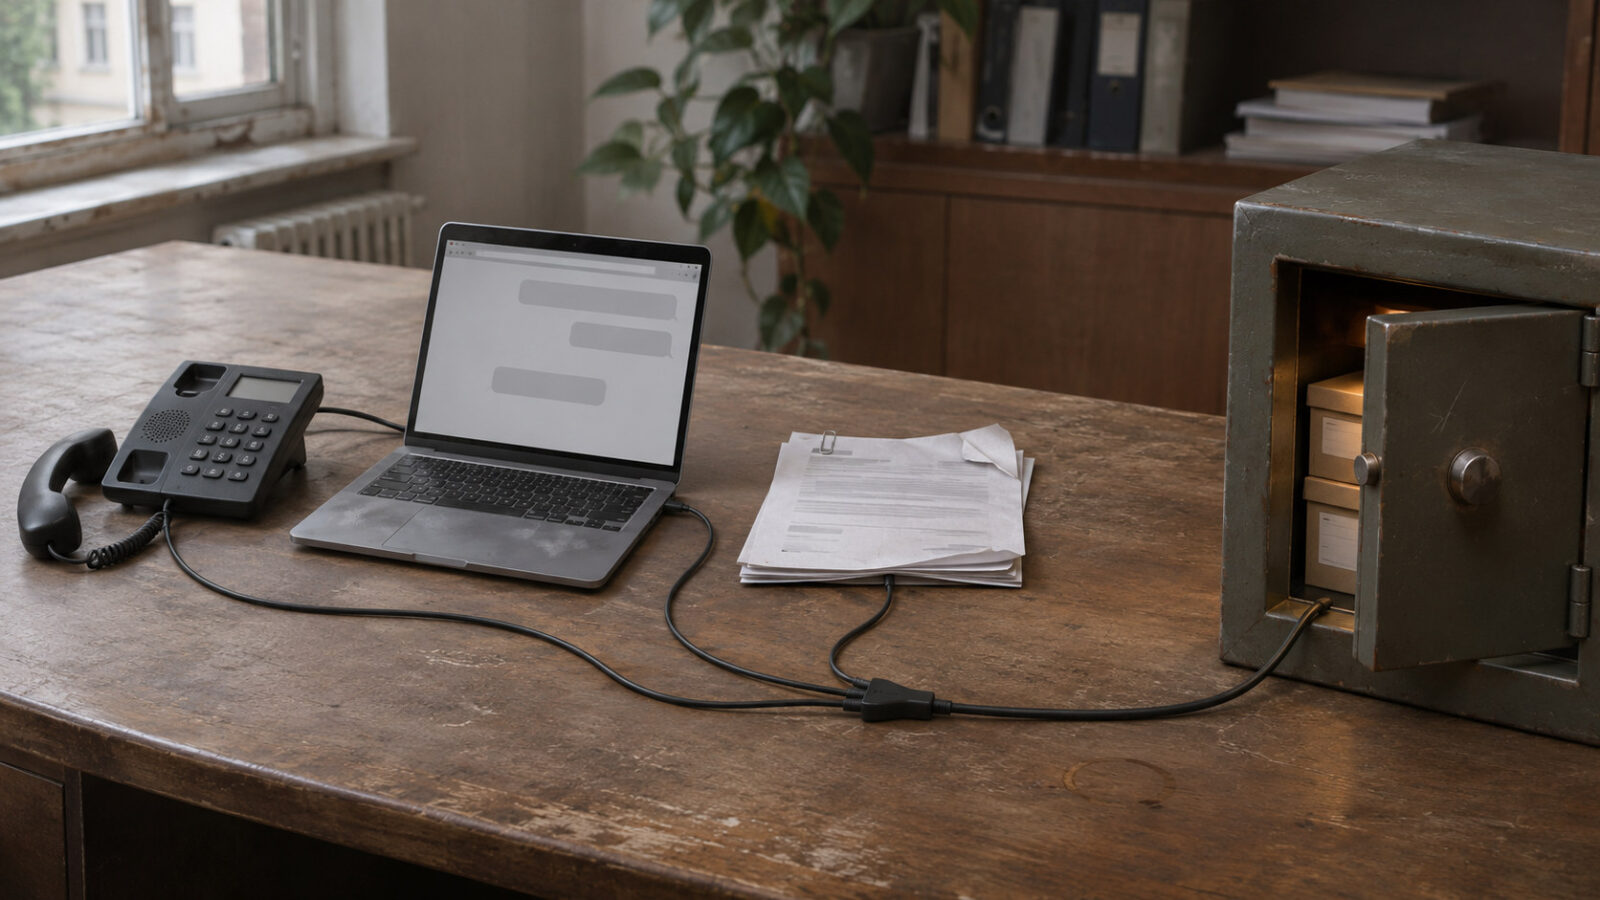
A call comes in through the cloud contact centre the organisation has contracted. A chat takes place on a SaaS digital customer service platform. An email passes through a hosted mail service. Each of these interactions is processed in a system the organisation does not control and, by default, that is also where it is stored. Nobody decided this. It happened because each supplier stores what it processes, and because storing it elsewhere takes extra effort. It is worth asking whether this is really how it should be.
In most organisations, the interaction history is spread across as many places as there are communications solution suppliers. Voice recordings sit with the operator or the telephony platform; chats, in the digital customer service tool; emails, in the mail service. Each of these systems lives in a public cloud, under the contract, retention policies and commercial life cycle of whoever runs it.
This history has two characteristics that rarely come together in the same asset: it is sensitive and it is vital. Sensitive, because it contains personal data, decisions, complaints, orders and commercial information. Vital, because it is the evidence of what was said, promised and agreed, and because the law requires it to be kept. MiFID II requires recordings to be kept for five years, extendable to seven at the request of the competent authority; the GDPR requires that period to be justified and the data to be deleted once it ends. An asset of this weight should not, by default, live where it was created.
No, and this is the distinction that solves the problem. Processing an interaction means routing the call, presenting the chat to the agent, delivering the email. It is a transient function that ends when the interaction ends. Preserving means storing that interaction intact, searchable and auditable for years. They are different functions, with different requirements, and there is no technical reason for the same supplier to perform both.
When the two are conflated, the communications supplier becomes, without anyone having appointed it, the custodian of the organisation’s compliance archive. The contract signed to handle calls also becomes the contract that governs the evidence. It is a dependency that arises by default and that few have documented.
The systems that process interactions can change whenever the business wants. The archive that preserves them should never change. Putting the two in the same place forces a choice between agility and continuity.
A centralised archive, under the organisation’s control, into which voice, chat and email from all suppliers converge, brings benefits that add up:
It does, and it is one of the most underestimated effects. Today, switching contact centre platform or operator means negotiating the export of years of recordings, in a format the new supplier may not read, with metadata that may not survive the migration. Many organisations postpone the change not because the current supplier is good, but because the history is locked in there.
When the archive is on your side, the decision to change supplier becomes a commercial and technical decision again, not a decision about the continuity of the evidence. The new system connects to the same archive and the history remains intact. DORA, moreover, requires financial entities to have documented exit strategies for critical ICT suppliers. A supplier-independent archive is the simplest way to have an exit strategy that actually works.
A SaaS communications platform can become unavailable, suffer a security incident, be acquired, change its terms or shut down. That platform’s resilience is not controlled by the organisation using it, however robust the SLA. If the archive is inside it, unavailability of the customer service is, at the same time, unavailability of the evidence.
With the archive in-house, a supplier failure interrupts customer service for a few hours, which is an operational problem. It does not interrupt access to five years of interactions, which would be a regulatory problem. The difference between the two situations is the difference between an incident you manage and an incident you report.
No. The problem is leaving the retention archive coupled to the system that processed the interaction, whether it is in the cloud or not. An organisation can quite legitimately host its centralised archive in a private or national cloud, provided the control, the keys and the jurisdiction are its own. What it should not do is accept, by default, that its customer history is split across several telecommunications suppliers, each keeping its own piece and none answering for the whole.
Conversations can, and will, continue to travel through the cloud. There is only one question: once they have travelled, do they come home?
No. The operator or contact centre platform processes the call, but the organisation can, and for compliance purposes should, keep the recording in its own archive, under its control, with its own retention and access policy.
It is a single repository, governed by the organisation, into which all customer interactions converge, regardless of channel (voice, chat, email) and of the supplier that processed them. It allows a single security, retention and audit policy to be applied to the entire history.
MiFID II requires five years, extendable to seven at the request of the competent authority. The GDPR requires the period to be justified and the data to be deleted at the end.
No. The archive can live on the organisation’s own infrastructure, in a private cloud or in a national cloud. What matters is that it is decoupled from the suppliers that process the interactions and that the organisation controls where it lives and who accesses it.
Published by the uPlayback team, a Grupês product. Three decades of experience in compliance recording.
Continue reading
Compliance, integrations and deployment answered live, with your questions on the table and no generic pitch.